Agentic AI vs RPA in Banking Operations
Confusing these tools wastes millions in deployment when the wrong one lands on the wrong job.
Banks keep treating agentic AI as a smarter version of RPA. That mistake is costing real deployment time, because the two run on opposite design principles. RPA follows a script exactly as written. Agentic AI figures out its own path toward a goal. Confuse the two, and you'll put the wrong tool on the wrong job, then wonder why the results fall flat.
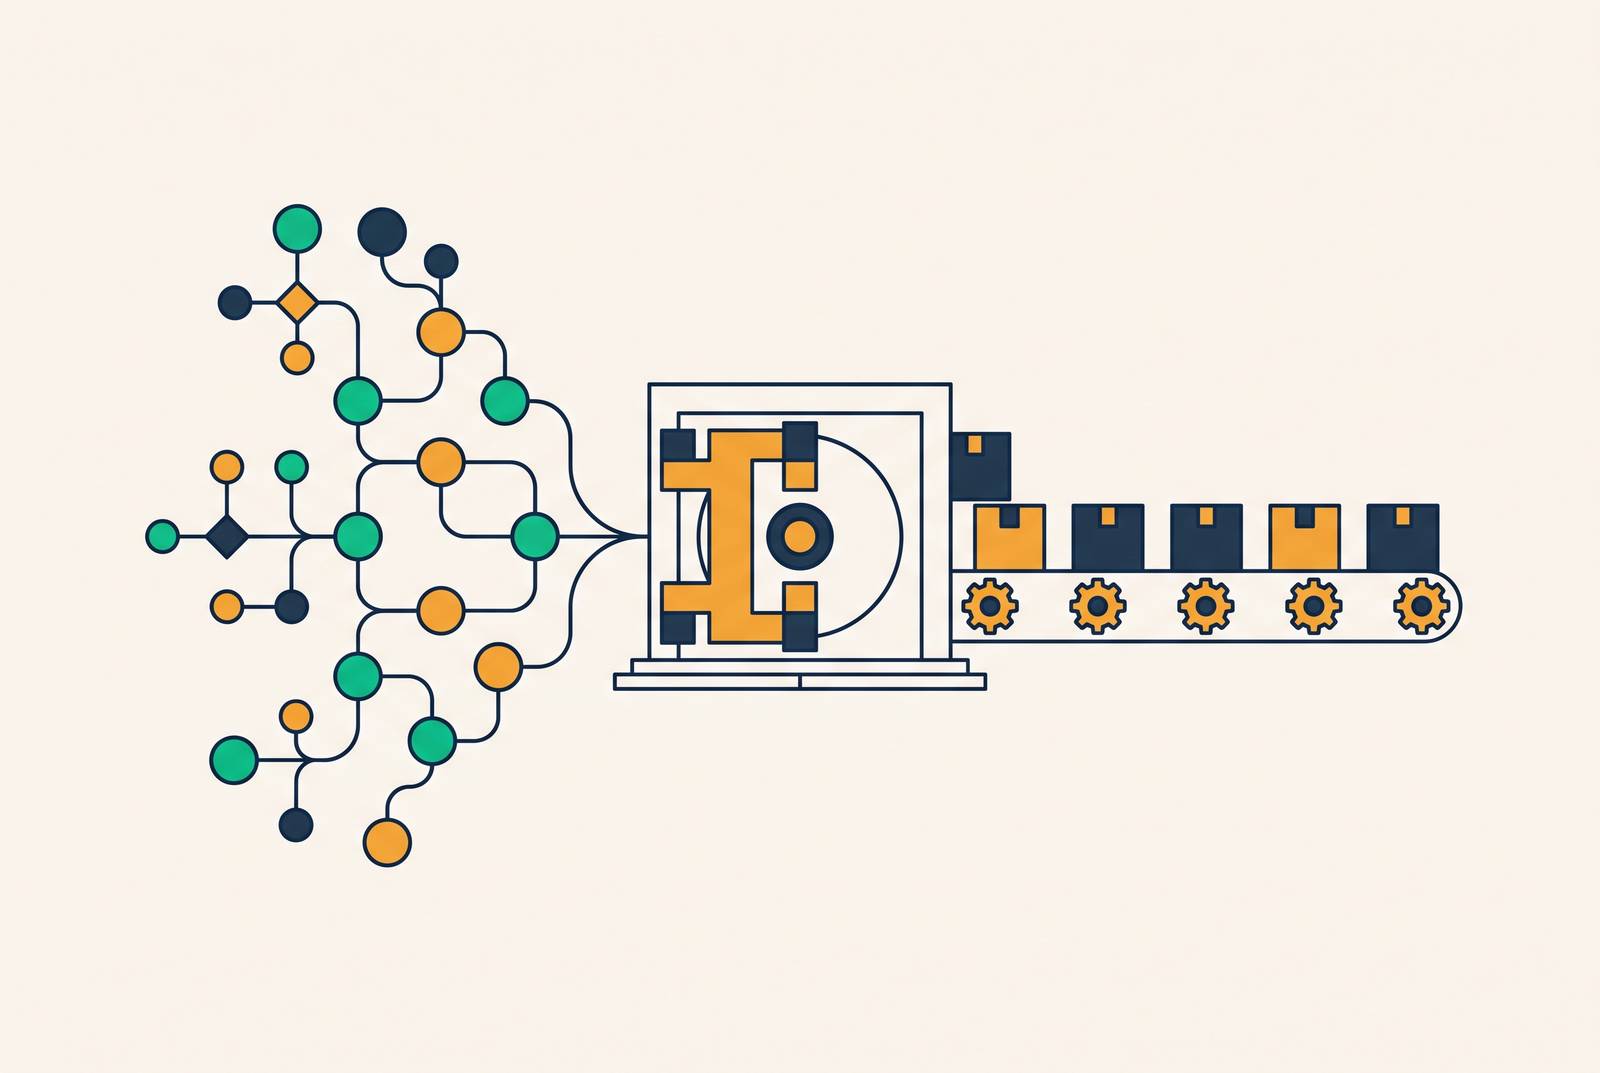
Start with what RPA actually is. Its whole design principle fits in four words: do these steps exactly. Fixed script, fixed sequence, fixed output every time. If a data field moves or a form changes shape, the bot breaks. It doesn't guess and it doesn't adapt; it stops and waits for a person to fix it and restart the process. Predictability was the whole point.
Agentic AI runs on a different instruction: achieve this goal, however you get there. It reads unstructured data, plans out multi-step tasks, and adjusts when conditions change. It works alongside people, flagging what needs a human look and handling the rest on its own.
Picture the banking automation stack in three layers. RPA sits at the execution layer: moving data, clicking through screens, posting transactions. Generative AI sits at the insight layer: it surfaces patterns and drafts recommendations but doesn't act on them. Agentic AI sits at the decision and orchestration layer: it figures out what should happen next and coordinates across systems to make it happen, managing exceptions as it goes. Mix these layers up and you end up buying an agent to do a script's job, or asking a script to make judgment calls it was never built for.
What RPA does well in banking and where it reliably breaks down
RPA earns its keep in work that's high-volume, stable, and governed by clear rules: posting journal entries, generating regulatory reports, reconciling accounts at the end of the day. Every step is scripted and logged, so the audit trail practically writes itself. A regulator can trace the exact path a transaction took, click by click. The vendor ecosystem here is mature, the risk profile well understood, and the integration patterns on legacy cores have been worked out over years of use.
Put RPA in front of anything with variability, judgment, or unstructured input, though, and it stalls. Exception handling shows this most clearly: RPA has no built-in way to decide what to do when a case falls outside its script. It just stops, or throws an error and waits for someone to notice.
KYC and AML reviews expose the limit even more sharply. That work means reading documents, reading intent, and cross-checking facts across multiple sources, none of which a scripted bot can do on its own. Banks currently put an estimated 10 to 15% of their full-time staff toward KYC and AML work alone, and still catch only around 2% of global crime flows moving through the system. Those two numbers together say something blunt: rule-based automation has a ceiling, and banks have already hit it.
Fraud detection runs into the same wall. Static rule sets miss novel schemes almost by definition, because RPA checks for what it was told to check and nothing else. In mortgage lending, a human underwriter grinding through 8 to 10 files a day is, in effect, doing all the exception-handling that scripted automation was never built to do.
There's also a maintenance cost that rarely shows up in the original ROI math. Every core system upgrade, every form revision, every vendor update carries a chance of snapping a script somewhere in the chain. In large deployments, bot maintenance turns into a job of its own, and the old "set it and forget it" pitch doesn't survive contact with how banking operations actually run day to day.
What agentic AI can do that scripted automation structurally cannot
Here's the core difference: agentic AI can read something unstructured, plan a sequence of actions around it, carry those actions out across several systems, and change course mid-task if something shifts, all inside one workflow. RPA can only do the first step it was told, then the next, then the next.
Mortgage underwriting shows the gap most clearly. With agentic AI handling document reading, data extraction, and rule application, roughly 95% of standard applications move through without a human touching them at all. The underwriter's job shifts from grinding through 8 to 10 files a day to reviewing 30 to 40, spending that freed-up time only on exceptions and genuinely hard cases. The agent isn't just executing steps; it's reading what's in front of it and deciding what matters.
Fraud detection benefits the same way. Agentic systems continuously map customer behavior and network connections, flagging schemes in real time that nobody wrote a rule for yet. RPA's static rule list, by definition, can't catch what it was never told to look for. That gap alone is worth sitting with: a fraud team that only automates the known patterns is admitting it can't touch the unknown ones.
Credit risk management gets a similar upgrade. Instead of waiting on a quarterly model refresh, an agentic system can recalibrate risk profiles as new data comes in, adjusting credit limits, repricing loans, or flagging early delinquency risk on its own.
Then there's the question of what happens when something breaks mid-process. A missing data field or a system that's briefly down would stop an RPA bot cold. An agentic system can often route around the obstacle or escalate the case with some judgment attached, instead of just erroring out. McKinsey's 2025 Global Banking Annual Review puts the productivity opportunity from AI and automation across banking at $200 to $340 billion a year. That range says something about what opens up once AI moves from surfacing insight to actually acting on it.
How governance requirements differ between the two automation types — and why that gap matters for banks
RPA governance is close to simple. Every step is scripted and logged by a human author, so the audit trail is, quite literally, the script itself. Nothing emergent happens, so nothing needs explaining beyond what's already written down.
Agentic AI's behavior comes from a goal rather than a fixed path, and the agent picks its own route to get there. That means regulators now need to see not just what happened, but why the system chose that particular path over another one. Model explainability, bias prevention, and data lineage stop being background assumptions and become things a bank has to actively demonstrate. Across the industry, data privacy exposure, AI hallucination in financial decisions, and lack of explainability have emerged as leading concerns for firms integrating AI into their operations.
What's striking is how regulators in different countries, without coordinating, are converging on the same worries. Regulators have flagged model risk, cybersecurity exposure, and compliance risk tied directly to AI use. Some regulators have reframed AI primarily as an ICT risk management issue rather than mainly an ethics question. Several regulators have moved toward requiring human involvement in any AI touching credit approval, account opening, or payment transactions. The EU AI Act imposes formal requirements on high-risk AI systems, including conformity assessments. And in the US, US regulators have signaled that institutions should demonstrate accuracy, transparency, and auditability rather than just avoid the technology altogether.
Before any agent gets connected to core banking functions, three things need to already be in place. An API abstraction layer that exposes core functions as clean, controlled endpoints instead of raw system access, comes first. Role-based identity and access controls, so the agent can only touch what it's explicitly allowed to touch, comes second. Immutable audit logging, so every action the AI takes on a core system leaves behind a record a regulator can actually read, comes third.
McKinsey's 2026 survey found only about a third of organizations report mature governance in place. That gap between what the technology can do and what governance can currently support is the real deployment risk right now, not the technology itself.
Why deterministic execution still has a mandated role in payment and transfer workflows
For payment execution specifically, regulators want a step-by-step record of exactly what happened and why it happened that way. Scripted, deterministic automation delivers that by design, and nothing about agentic reasoning replaces that requirement.
That's why smart payment architecture splits the labor instead of picking one tool for the whole job. Agentic AI handles reasoning and prep: it reads the payment instruction, checks it against policy, spots exceptions, and escalates anything unclear. RPA or a rules engine then handles final execution, carrying out the approved transaction on the rail and generating the immutable record regulators expect.
This split isn't a compromise; it's the architecture that satisfies what regulators require while keeping the intelligence layer intact. UiPath's model for banking automation shows this pattern in practice: agentic AI adjudicates alerts, summarizes the evidence behind a decision, and writes audit-ready narratives, while RPA and AI run as one governed workflow instead of two tools competing for the same job.
Voice and text interfaces fit the same pattern. A customer can start and confirm a real transaction, a payment, a transfer, an account change, through a conversational interface, while the execution underneath stays auditable and rule-governed the whole time. The conversation flexes; the execution underneath it doesn't.
Banks and credit unions that get this division right don't have to sit around waiting for every open governance question about full autonomous execution to get settled. They can put agentic AI to work on high-value judgment tasks now, and let deterministic systems keep handling the parts regulators need locked down.
Where the layered model works in practice — and what adoption actually looks like
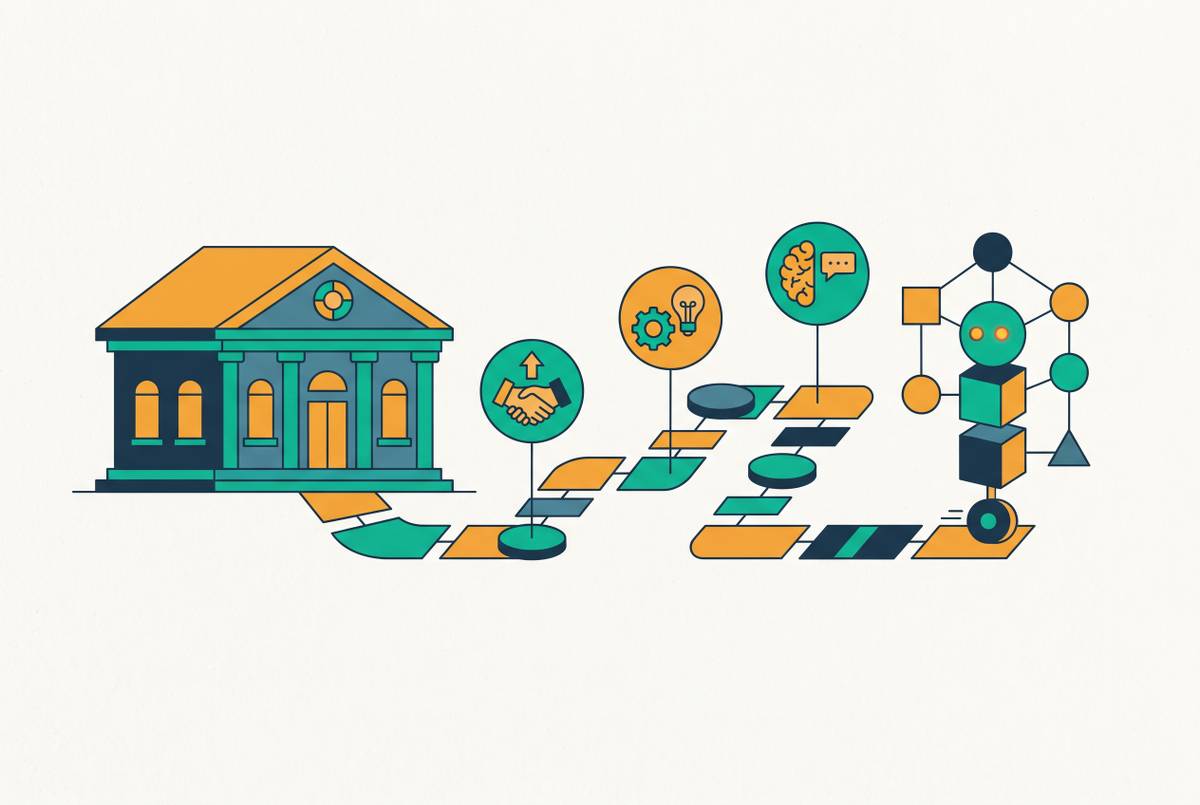
Most banks past the pilot stage have landed on a layered setup: RPA runs execution, agentic AI runs decision-making and orchestration above it. That's likely the architecture that sticks, especially in a regulated environment where an audit trail isn't optional.
Cobalt Credit Union, based in Nebraska and serving a military-rooted membership spread across every US state and more than 20 countries, didn't roll out agentic AI in one big announcement. It came together over a multi-year sequence of deployments, which is a far more honest picture of how financial institutions actually adopt this technology than any single splashy go-live story suggests.
Credit unions, in fact, appear to be moving faster than the bigger-bank narrative would have you believe. As of 2026, 59% of credit unions have deployed generative AI in some form, a 10-point lead over banks at 49%, according to Cornerstone Advisors' What's Going On in Banking 2026 survey of 416 senior executives. Staffing pressure and rising member expectations seem to be what's pushing credit unions to move fast. The segment overall is expected to grow at a 41.5% compound annual rate through 2034.
The vendor landscape built specifically for banking-grade agentic AI is maturing fast too. Backbase launched its AI-native Banking OS in April 2026, running above cores, payments, and CRM systems, with a "Sentinel" authority layer that checks every actor's permissions against bank policy before anything executes, then logs each action afterward. It already serves more than 120 financial institutions, including Navy Federal Credit Union, TD Bank, and KeyBank. In lending verification specifically, Informed.IQ has built vertical agents trained on a proprietary dataset drawing from over 100 million loan documents and more than 2 billion data points; the company raised $63 million in December 2025. Other vendors are also active in this space, building out banking-specific capabilities of their own. The compliance-ready end of the market is characterized by payments and transaction automation running on existing rails, configurable controls, and full audit trails.
Contact centers, underwriting, and fraud detection are widely identified as the best places to start. These are mature use cases where the payoff from adding a reasoning layer is clearest, and where the governance requirements are already fairly well understood.
How to decide which automation type belongs in which part of a banking operation
Here's the diagnostic question, and it's worth asking out loud before any deployment decision: does this process need judgment, variable inputs, or exception handling? Or does it need deterministic, auditable execution of a sequence that's already known? If it's the former, agentic AI belongs somewhere in the loop. If it's the latter, RPA or a rules engine is the right call, maybe with an agent sitting upstream to handle orchestration.
Sort the work into rough buckets and the fit gets obvious fast. High-volume, stable, fully structured work, end-of-day reconciliation, report generation, posting data in a known format, is low-risk territory for RPA and should stay there. Judgment-heavy work with structured outputs, underwriting decisions, fraud escalation, credit limit changes, calls for agentic AI at the decision layer paired with deterministic execution underneath. Unstructured input carrying regulatory weight, KYC document review, AML pattern analysis, dispute investigation, needs agentic AI with a human sitting at every decision point, not an optional check bolted on later. Customer-facing transaction requests through voice or text, payments, transfers, account questions, fit a conversational agentic interface running on top of controlled, existing execution rails.
Governance readiness has to come before deployment, never after. API abstraction, role-based access controls, and immutable audit logging need to exist before an agent ever touches a core system, not get bolted on once something's already gone wrong. SOC 2 certification and demonstrable compliance readiness are the floor for any vendor in this space, not a differentiator worth bragging about. The real question isn't whether to deploy agentic AI at all; it's how to scope that first deployment narrow enough that governance can be shown to work from day one.
The market context makes the timing question harder to ignore. The agentic AI market for banks and credit unions was valued at $4.8 billion in 2025 and is projected to reach $78.6 billion by 2034, a 38.2% compound annual growth rate. Treating this as a future-state decision, something to revisit next year or the year after, is simply a timing error.
So what does outgrowing RPA actually look like in practice? The scripts mostly stay exactly where they are, still executing the same steps they always did. What changes is who decides which script runs, when, and why. That decision increasingly belongs to the agent sitting above it, not the person who used to make the call by hand.